
Static values (OIDC) - Test only
Sammanfattning av användningsfall
Scenario
Section titled “Scenario”In this scenario, we will use Postman acting as a OIDC Relying Party (RP) and Integrity Web as an OpenID Connect Provider (OP). The guide is done for a Windows installation but can be changed for Docker and Linux installations as well.
Authentication will be done with static values.
Prerequisite
Section titled “Prerequisite”There are some prerequisite for this use case. You will need the following:
- Server platform. Docker, Windows or Linux. In this use case we have used a Windows server.
- The current version of FortifiedID Integrity Web is installed.
- Basic knowledge about Postman and Postman installed on the local computer with access to the Integrity server. You will also need the following preconfigured Postman Collection https://download.fortifiedid.se/FID.postman_collection.zip
Note. All configuration and testing is done on the scenario server.
Configuration
Section titled “Configuration”Download and modify configuration
Section titled “Download and modify configuration”- To download the ZIP file containing the configuration and all other necessary files for Integrity Web, click USE_CASE_LINK to download the customer folders for the web..
- Copy the customer_WEB folder to you \..\fortifiedid\web\ folder.
Rename the existing customer folder tocustomer_ORGand renamecustomer_Webto customer.
Update the configuration to map to your environment
Section titled “Update the configuration to map to your environment”The downloaded folders contains all needed files. For example, test certificates files are included and configured to work with the example application.
However, some data needs to be changed to map your environment. Since this example was done on a Windows server you might need to update file paths if you run something else. Also the http ports might need to be changed if they are not available in your environment.
To make it easy the application folder have a file called globals.json that contains the data you need to change. Config.json uses the variables in globals.json.
- Open globals.json for \..\fortifiedid\enrollment\customer\config and \..\fortifiedid\web\customer\config folder and update:
- File paths
- HTTP if needed
- When updated, start the Integrity Web service.
- Wait until Integrity Web service has started before continuing.
Test the use case
Section titled “Test the use case”OIDC well-known information
Section titled “OIDC well-known information”- Open a browser on the Integrity Web server
- Browse to https://localhost:8443/oidc/tenant1/.well-known/openid-configuration
- Verify that the well-known page opens
Use Postman to test the OIDC flow
Section titled “Use Postman to test the OIDC flow”-
Download the file https://download.fortifiedid.se/FID.postman_collection.zip
-
Unzip the file and import the collection to Postman.
The collection will be called "FID-OIDC-UseCases" in Postman -
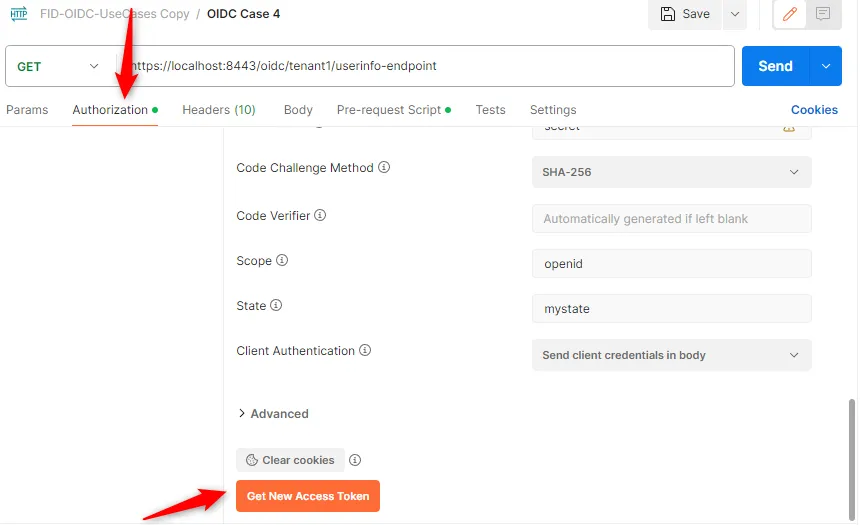
Open the Request "OIDC Case 4" in the "FID-OIDC-UseCases" collection
-
Select the Authorization tab of the request
-
Click on the button "Get New Access Token"
-
Enter username and password.
-
Copy the content of the ID-token and verify the content by pasting the content in the Encoded frm of the web page https://jwt.io/
Complete config.json file
Section titled “Complete config.json file”The config.json for Integrity Web can be found in the included ZIP file associated with this use case.
{ "globals": "@include:globals.json", "modules": [ { "name": "CefEventModule", "config": { } }, { "name": "OIDCModule", "enabled": true, "config": { "providers": [ { "http_context": "/oidc", "http_port": "${globals.http.port}", "http_use_ssl": true, "http_keystore_ref": { "type": "${globals.keystore.https.ref.type}", "path": "${globals.keystore.https.ref.path}", "password": "${globals.keystore.https.ref.password}" }, "http_keystore_type": "${globals.keystore.https.type}", "http_key_alias": "${globals.keystore.https.http_key_alias}", "http_key_password": "${globals.keystore.https.http_key_password}", "discovery_meta": { "issuer": "${globals.oidc.op1.oidc_op_address}/oidc/tenant1", "authorization_endpoint": "${globals.oidc.op1.oidc_op_address}/test/authn/oidc", "token_endpoint": "${globals.oidc.op1.oidc_op_address}/oidc/tenant1/token-endpoint", "userinfo_endpoint": "${globals.oidc.op1.oidc_op_address}/oidc/tenant1/userinfo-endpoint", "jwks_uri": "${globals.oidc.op1.oidc_op_address}/oidc/tenant1/.well-known/openid-configuration/jwks", "end_session_endpoint": "${globals.oidc.op1.oidc_op_address}/test/authn/oidc/logout", "scopes_supported": [ "openid" ], "response_types_supported": [ "code" ], "grant_types_supported": [ "authorization_code" ], "subject_types_supported": [ "public" ], "id_token_signing_alg_values_supported": [ "RS256" ], "token_endpoint_auth_methods_supported": [ "client_secret_post", "client_secret_basic" ], "claims_supported": [ "iss", "ver", "sub", "given_name", "family_name" ], "request_parameter_supported": true }, "tenant_op_path": "/tenant1", "keystore": { "path": "${globals.keystore.oidc.path}", "password": "${globals.keystore.oidc.password}", "type": "${globals.keystore.oidc.type}", "alias": "${globals.keystore.oidc.alias}" }, "sign_jwt_keystore_password": "${globals.keystore.oidc.password}", "sign_jwt_keystore_alias": "${globals.keystore.oidc.alias}", "rps": [ { "client_id": "${globals.oidc.op1.client_id}", "client_secret": "${globals.oidc.op1.client_secret}", "redirect_uri": [ "${globals.oidc.op1.redirect_uri}" ], "post_logout_redirect_uris": [ "${globals.oidc.op1.post_logout_redirect_uris}" ] } ] } ] } }, { "name": "AuthN", "enabled": true, "config": { "context_path": "/authn", "webroot_dir": "web", "http_port": "${globals.http.port}", "http_use_ssl": true, "http_keystore_ref": { "type": "${globals.keystore.https.ref.type}", "path": "${globals.keystore.https.ref.path}", "password": "${globals.keystore.https.ref.password}" }, "http_keystore_type": "${globals.keystore.https.type}", "http_key_alias": "${globals.keystore.https.http_key_alias}", "http_key_password": "${globals.keystore.https.http_key_password}", "authenticators": [ { "id": "oidc", "type": "OIDCAuthCodeFlow", "config": { "base_path": "/test/authn", "failure_location": "/authn/failure.html", "simple_logout": true, "required_request_parameters": [ "response_type", "client_id", "redirect_uri", "scope" ], "required_authenticators": [ "auth01" ], "jwt_headers": { "kid": "" }, "jwt_claims": { "secret_id": "{{{session.id}}}", "aud": "app", "sub": "{{{item.subject}}}", "nonce": "{{{request.nonce}}}", "test_boolean": true, "family_name": "{{{item.family_name}}}", "given_name": "{{{item.given_name}}}", "name": "{{{item.name}}}", "amr": "{{{item.amrRef}}}" }, "userinfo_claims": { "secret_id": "{{{session.id}}}", "userinfo_claim_test": "static_claim", "email_verified": true, "subject": "{{{item.subject}}}" }, "token_endpoint_ttl": 60000, "userinfo_endpoint_ttl": 60000, "keystore": { "path": "${globals.keystore.oidc.path}", "password": "${globals.keystore.oidc.password}", "type": "${globals.keystore.oidc.type}", "alias": "${globals.keystore.oidc.alias}" }, "sign_jwt_keystore_password": "${globals.keystore.oidc.password}", "sign_jwt_keystore_alias": "${globals.keystore.oidc.alias}", "rps": [ { "client_id": "${globals.oidc.op1.client_id}", "client_secret": "${globals.oidc.op1.client_secret}", "redirect_uri": [ "${globals.oidc.op1.redirect_uri}" ], "post_logout_redirect_uris": [ "${globals.oidc.op1.post_logout_redirect_uris}" ] } ] } }, { "id": "auth01", "type": "Selector", "config": { "base_path": "/test/authn", "webroot_dir": "web/authenticator/selector", "options": [ { "id": "1", "target": "oidc_static_1", "label": "Static User1" }, { "id": "2", "target": "oidc_static_2", "label": "Static User2" } ] } }, { "id": "oidc_static_1", "type": "NoOp", "config": { "base_path": "/test/authn", "subject": "Fortified ID test 1", "exports": [ { "name": "amrRef", "value": "static values" }, { "name": "given_name", "value": "Test1" }, { "name": "family_name", "value": "Fortified ID" }, { "name": "name", "value": "Test1 Fortified ID" } ] } }, { "id": "oidc_static_2", "type": "NoOp", "config": { "base_path": "/test/authn", "subject": "Fortified ID test 2", "exports": [ { "name": "amrRef", "value": "static values" }, { "name": "given_name", "value": "Test2" }, { "name": "family_name", "value": "Static" }, { "name": "name", "value": "Test2 Static" } ] } } ] } } ]}