
Inera IdP (SITHS) (SAMLSPBroker)
Scenario
Section titled “Scenario”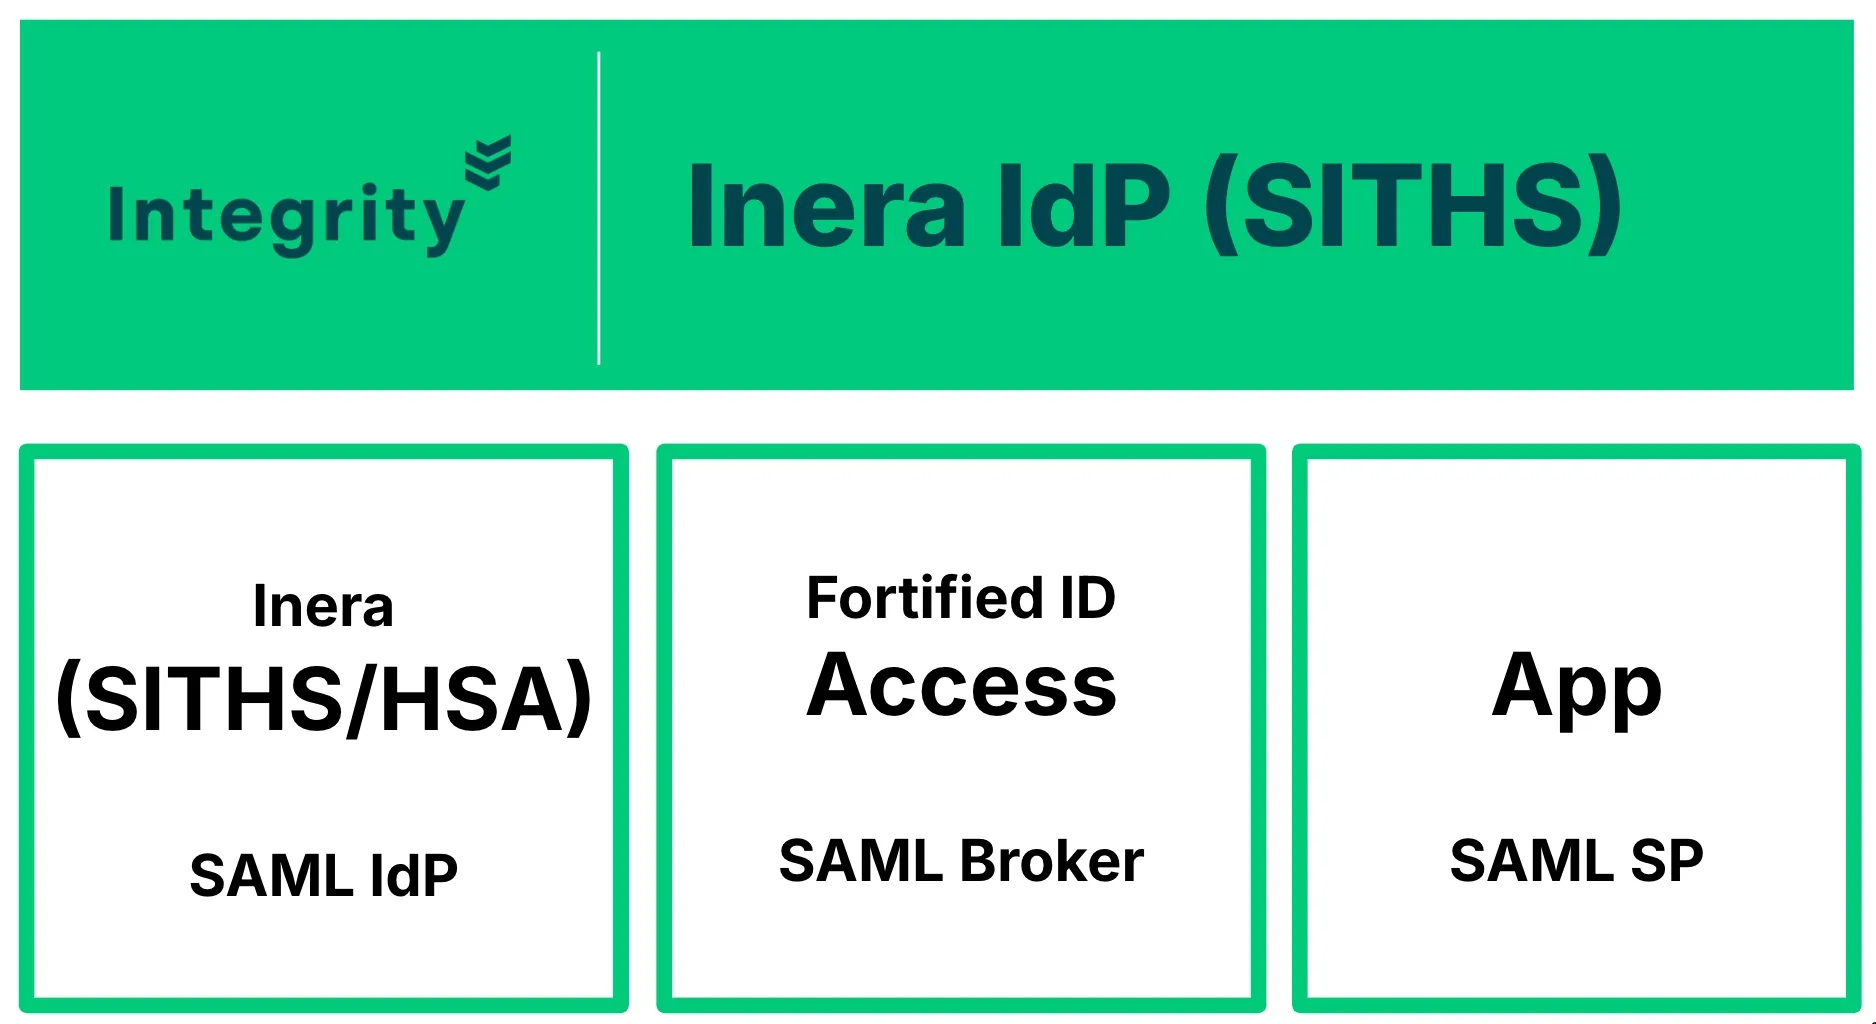
This use case contains configuration to add Inera IdP (which will provide SITHS verification) as an authentication method, using SAMLSPBroker.
The external SAML IdP is Inera IdP.
Fortified ID WEB will act as a SAML SP to Inera IdP.
Prerequisite
Section titled “Prerequisite”There are some prerequisite for this use case. You will need the following environment:
- This use case assumes that you have good knowledge of the product in question.
- Fortified ID WEB installed and configured.
Basic configuration of Fortified ID Integrity Web
Section titled “Basic configuration of Fortified ID Integrity Web”Add files and configuration
Section titled “Add files and configuration”- Add files and folders from ZIP-file to Fortified ID Integrity Web.
- Download the use case.
- Rename customer-inera-sp to customer
- Replace the customer folders for your installations with the ones from the zip-file.
- Open the globals_inera_sp.json file and the globals.json file
- Add the parameters missing in globals.json from globals_inera_sp.json.
- Change the newly added parameters to match your environment.
- Open the config_inera_sp.json file and the config.json file
- Add the configuration missing in config.json from config_inera_sp.json.
- Restart the Integrity Web service.
Extract metadata needed
Section titled “Extract metadata needed”- Open a browser and browse to https://INTEGRITY_HOST/saml/metadata/inerasp
- Download the metadata file
- Upload the file to https://validator.sambi.se/ and verify that there are no errors.
- Attach the metadata to the prestudy doc (Förstudie avseende anslutning till Legitimeringstjänst IdP för medarbetare) that must be sent to Inera for approval and trust.
Complete config_inera_sp.json file
Section titled “Complete config_inera_sp.json file”{ "globals": "@include:./globals.json", "modules": [ { "name": "HttpClient", "config": { "name": "default", "ssl_trust_all": true, "idle_timeout_ms": 5000, "connect_timeout_ms": 5000 } }, { "name": "SAML", "config": { "http_port": "${globals.http.port}", "enable_http": true, "metadata_cache": "${globals.base_dir}/config/resources_internal/saml_cache/", "metadata_template": [ { "id": "inerasp", "metadata_file_path": "${globals.base_dir}/config/resources_internal/saml_templates/inera_sp_metadata_template.xml", "sign_ref": [ { "keystore": { "path": "${globals.keystore.path}", "password": "${globals.keystore.password}", "alias": "${globals.keystore.alias}", "key_password": "${globals.keystore.key_password}" } } ] } ], "metadata": [ { "url": "https://idp.inera.se/saml" } ] } }, { "name": "AuthN", "enabled": true, "config": { "context_path": "/saml/authn", "webroot_dir": "web", "http_port": "${globals.http.port}", "authenticators": [ { "id": "inerasp", "type": "SAMLSPBroker", "config": { "base_path": "/saml/authn", "issue_as_sp_entity": "https://${globals.host}/saml/inerasp", "target_idp_entity": "https://idp.inera.se:443/saml" } } ] } } ]}Complete globals_inera_sp.json
Section titled “Complete globals_inera_sp.json”{ "base_dir": ".", "host": "be4f-194-68-171-97.ngrok-free.app", "http": { "port": 8443 }, "keystore": { "https": { "ref": { "type": "JKS", "path": "${globals.base_dir}/config/resources_internal/certificates/server.jks", "password": "1234" }, "type": "JKS", "http_key_alias": "server", "http_key_password": "1234" }, "alias": "1", "key_password": "1234", "password": "1234", "path": "${globals.base_dir}/config/resources_internal/certificates/fortifiedid.p12" }, "inerasp": { "Company": "My Company", "GivenName" : "John", "SurName" : "Brown", "EmailAddress" : "[email protected]", "TelephoneNumber" : "012345678", "OrganizationName" : "My Company", "OrganizationDisplayName" : "My Company", "OrganizationURL" : "https://mycompany.com" } }