
Introduction
Overview of Pipes functionality, strengths, and how administrators use it.
Pipes is Fortified Integrity's configurable process engine for multi-step integrations and automation flows. It lets administrators connect validation, transformation, lookups, external API calls, directory operations, notifications, and other actions into a single controlled execution path without writing custom application code for each use case.
A pipe consists of an ordered list of valves. Each valve performs one task, and the pipe executes them from top to bottom. The result is a reusable, traceable, and centrally managed process that can receive input, work with session and flow data, call external systems, and return a structured result to the caller.
| Configuration See how the module, pipes, and valves are configured. | Valves Browse the available valve categories and their configuration. |
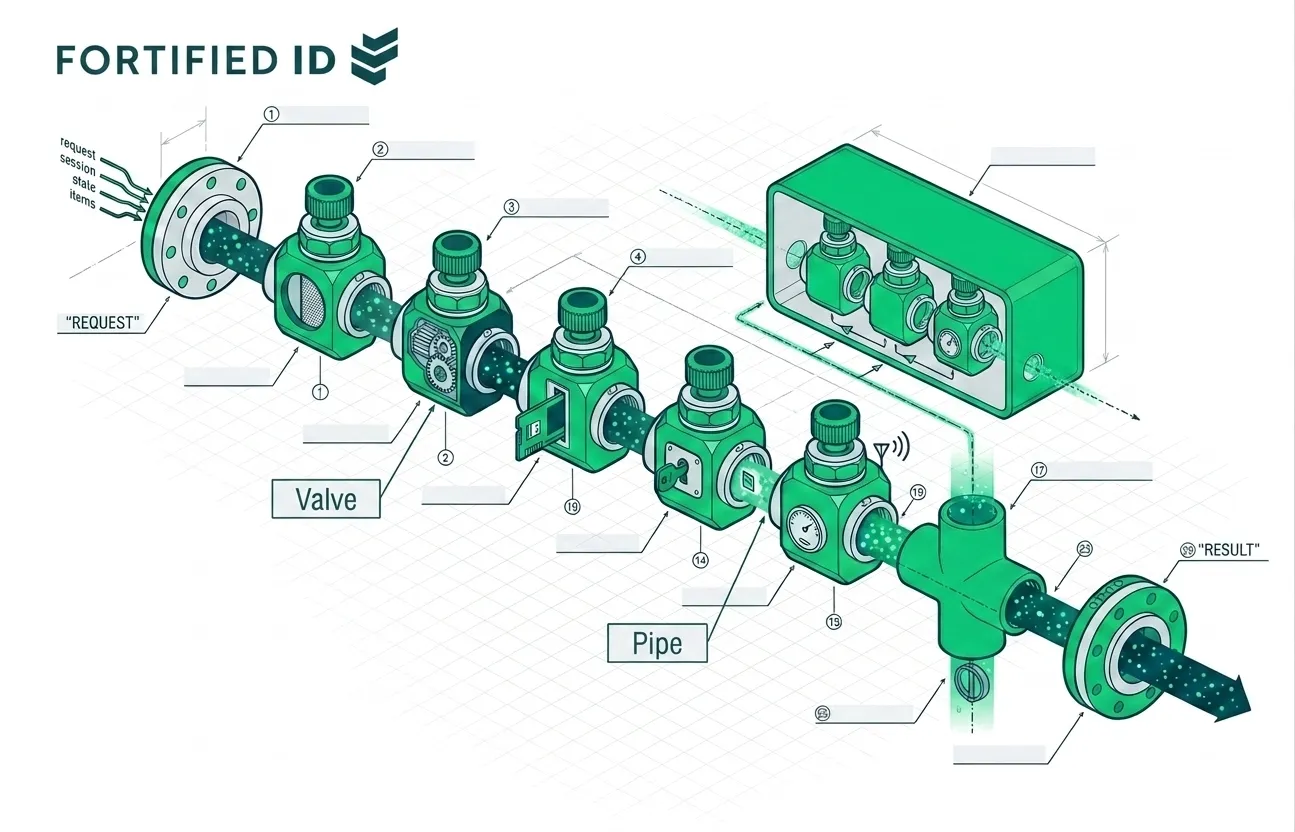
A pipe and its valves
What Pipes is used for
Section titled “What Pipes is used for”Administrators typically use Pipes when an incoming request needs to be processed through several coordinated steps such as:
- validating request data
- enriching information from LDAP, Entra ID, HTTP APIs, JDBC, or other sources
- transforming values into the format required by the next system
- applying conditional flow control based on the current state
- generating documents, tokens, passwords, or other artifacts
- sending notifications through SMS, voice, or SMTP
- reusing shared logic by calling other pipes
This makes Pipes suitable for identity-related orchestration, integration glue, approval preparation, data normalization, and operational automation where consistency and reuse matter.
Strengths for administrators
Section titled “Strengths for administrators”Pipes is especially strong in environments where administrators need to maintain automation over time without turning every change into a development project.
- Configurable orchestration: complex flows can be assembled from smaller reusable steps
- Integration breadth: one pipe can combine directory operations, HTTP calls, item handling, security functions, messaging, and transformation logic
- Operational flexibility: changes can often be made by adjusting pipe or valve configuration rather than changing application code
- Reuse and standardization: common logic can be reused through shared valve patterns and pipe-to-pipe calls
- Controlled execution: request data, session data, state, items, exports, and flow control are handled within one consistent runtime model
- Clear troubleshooting model: a failing process can be understood as a sequence of named valves rather than an opaque custom integration
How execution works
Section titled “How execution works”At runtime, Pipes creates a new flow for each pipe invocation.
- A caller invokes a named pipe and provides request data.
- Pipes creates a flow context that can include request, session, state, items, and exports.
- Valves execute in the configured order.
- Each valve can read from the current context, write new values, call external systems, or control the next step in the flow.
- When execution is complete, the caller receives a result containing status and additional data from the flow.
This execution model makes it easier to reason about processes, because each valve has one clear responsibility and each pipe expresses the full sequence explicitly.
Terms and abbreviations
Section titled “Terms and abbreviations”| Value | Description |
|---|---|
| Pipe | An ordered sequence of valves that can be executed. |
| Flow | The runtime representation of a pipe. When a pipe is called a new flow is created. The flow contains information about the current execution and a context containing the request parameters (if any), the current session (if any) and state common to all valves in the current flow. |
| Valve | Executable component that provides the functionality of a pipe. |